
Cybersecurity protection has become an essential part of everyday digital life. Every time you browse a website, send an email, shop online, or access a business account, your information may face potential security risks. Hackers and cybercriminals constantly look for weaknesses in devices, networks, and online systems, making digital security important for individuals and businesses.
Understanding what cybersecurity protection is can help you recognize online threats and take practical steps to protect sensitive information. From strong passwords and secure networks to antivirus software and data encryption, different security measures work together to reduce cyber risks. These protections help keep personal information, business records, and digital services secure.
What Is Cybersecurity Protection?
Cybersecurity protection refers to the technologies, processes, and practices used to defend computers, networks, applications, and digital information against cyber threats. Its primary purpose is to prevent unauthorized access, data theft, system damage, and service interruptions. Businesses and individuals use cybersecurity measures to protect sensitive information and maintain safe digital environments during their everyday online activities.
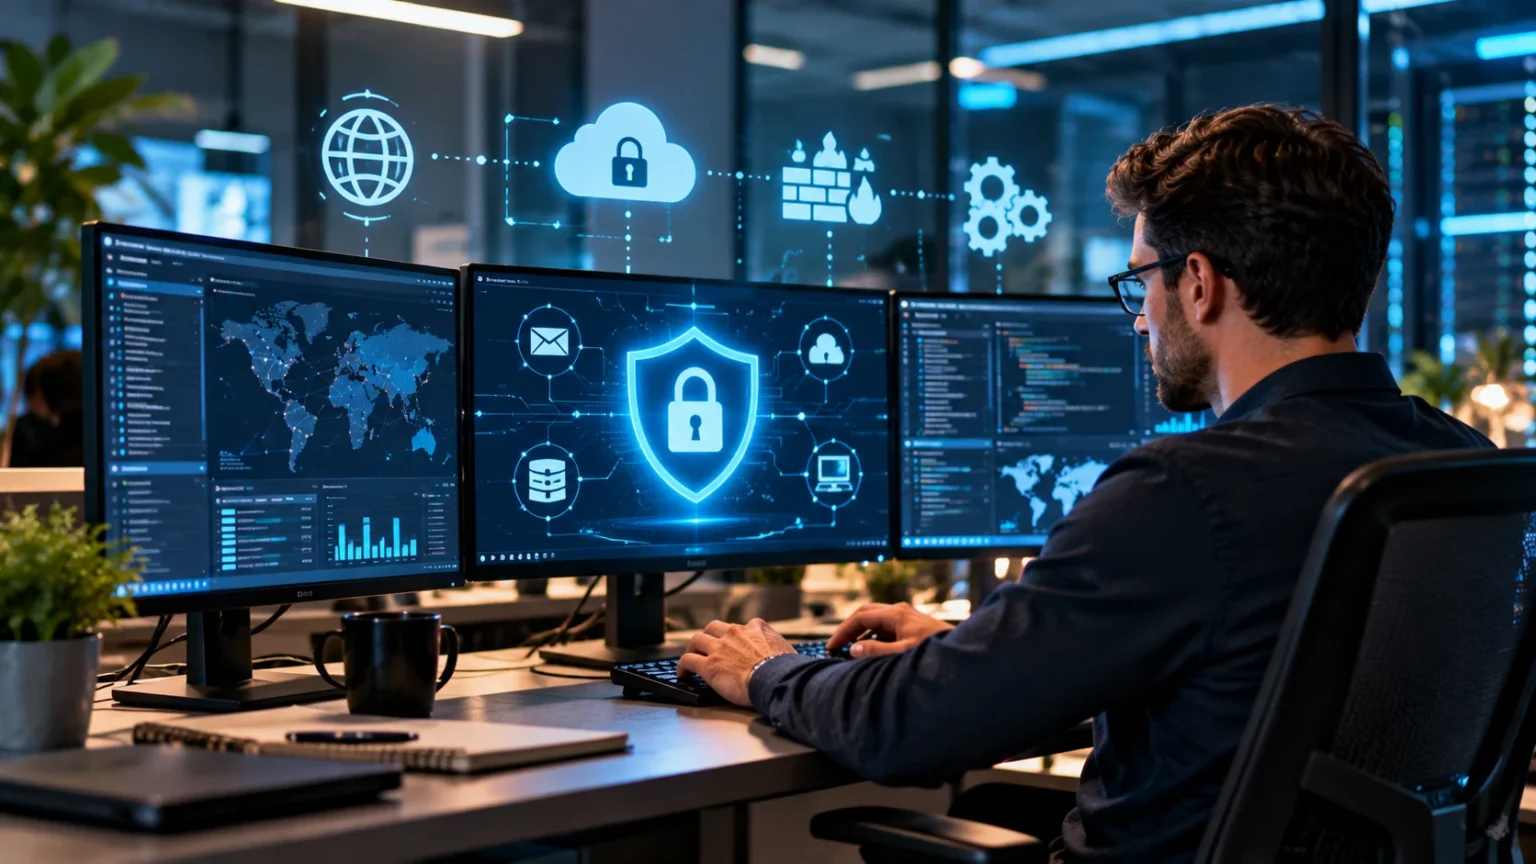
Cybersecurity protection involves several security layers working together to identify and reduce potential risks. These layers may include firewalls, antivirus tools, encryption, access controls, and continuous security monitoring. Each measure addresses different vulnerabilities within a digital system. When properly implemented, they make it more difficult for attackers to compromise devices, applications, and confidential business information.
For example, a company may use cybersecurity protection to secure employee accounts, customer records, and financial transactions. Individuals can protect themselves by enabling multifactor authentication, installing software updates, and avoiding suspicious links. Although no security system can eliminate every threat, effective cybersecurity practices significantly reduce exposure to common attacks and support safer online experiences.
Why Is Cybersecurity Protection Important?
Cybersecurity protection matters because people and organizations increasingly depend on digital technology for communication, financial transactions, and daily operations. Personal information, including passwords, contact details, and banking records, may be stored across multiple online platforms. Without appropriate security measures, attackers could access this information and use it for fraud, identity theft, or other harmful activities.
For businesses, a successful cyberattack can cause financial losses, operational disruptions, and damage to customer trust. A ransomware incident, for example, may prevent employees from accessing important files or business systems. Recovering affected services can require significant time and resources. Strong security practices help organizations reduce these risks and maintain more reliable business operations.
Cybersecurity also supports privacy and responsible information management. Customers expect businesses to handle their personal data carefully and prevent unnecessary exposure. Depending on the industry and location, organizations may have legal obligations to protect certain information. Implementing appropriate cybersecurity safeguards helps businesses meet relevant requirements while demonstrating a commitment to protecting customer and employee data.
How Does Cybersecurity Protection Work?
Cybersecurity protection works by identifying potential security risks and applying safeguards that reduce the likelihood or impact of attacks. These safeguards may operate across devices, applications, networks, and cloud services. Security teams often begin by assessing valuable information and possible vulnerabilities. They then choose controls that address the most important risks within their environment.
Prevention is an important part of cybersecurity, but effective protection also involves detecting suspicious activity. Firewalls can filter network traffic, while endpoint security tools may identify malicious software or unusual behavior. Monitoring systems can alert administrators when potentially harmful events occur. Combining these technologies helps organizations recognize threats before they cause more extensive damage.
Cybersecurity protection also includes responding to incidents and restoring affected systems. Organizations develop response procedures to investigate security events, contain threats, and recover important services. Regular data backups can help restore information after certain attacks or technical failures. This combination of prevention, detection, response, and recovery creates a more complete approach to digital security.
What Are the Main Types of Cybersecurity Protection?
Network security focuses on protecting communication systems and connected devices from unauthorized access and malicious activity. Common network protection measures include firewalls, secure network configurations, and intrusion detection systems. These technologies help control how information moves between devices and services. Network security is particularly important for organizations that connect numerous computers, servers, and business applications.
Endpoint security protects individual devices such as laptops, desktop computers, smartphones, and tablets. These devices may become entry points for attackers when they contain outdated software or unsafe applications. Antivirus programs, device encryption, and endpoint detection tools help reduce such risks. Keeping operating systems updated is another important part of maintaining effective endpoint protection.
Cloud security and application security address additional areas of digital infrastructure. Cloud security protects information and services hosted on remote computing platforms, while application security focuses on reducing weaknesses within software. Both involve measures such as access controls, security testing, and proper configuration. Together, these different cybersecurity categories help organizations protect information across modern technology environments.
Common Cybersecurity Threats You Should Know
Malware is a common cybersecurity threat that includes harmful software designed to damage systems, steal information, or perform unauthorized activities. Viruses, spyware, and ransomware are examples of different malware categories. Some malicious programs attempt to collect confidential information, while others interfere with normal system operations. Updated security software and careful downloading habits can help reduce exposure.
Phishing attacks attempt to trick people into revealing passwords, financial information, or other sensitive details. Attackers may send emails or messages that appear to come from trusted organizations. These messages often encourage recipients to click suspicious links or open unexpected attachments. Recognizing unusual requests and verifying information through official channels can help prevent phishing-related security incidents.
Other cyber threats include stolen passwords, account takeovers, denial-of-service attacks, and exploitation of software vulnerabilities. Attackers may target weaknesses in online accounts or systems to gain unauthorized access. Some attacks focus on stealing information, while others aim to interrupt services. Understanding these threats helps individuals and organizations select appropriate cybersecurity protection measures for their specific needs.
Essential Cybersecurity Protection Tools and Technologies
Firewalls are widely used cybersecurity tools that help control incoming and outgoing network traffic. They examine communication according to configured security rules and can block certain unauthorized connections. Firewalls are commonly included in operating systems, routers, and business network environments. However, they should be combined with other protections because they cannot prevent every type of cyberattack.
Antivirus and endpoint security software help identify potentially malicious files, programs, and activities. Modern security products may include real-time scanning, behavior monitoring, and threat detection features. These tools can reduce exposure to known and some emerging threats. They work best when regularly updated and supported by safe browsing habits and properly maintained devices.
Encryption and multifactor authentication provide additional protection for sensitive information and online accounts. Encryption transforms readable information into a protected form that requires an appropriate key to access. Multifactor authentication adds another verification step beyond a password. Using these technologies together helps reduce the risk of unauthorized access, particularly when passwords or stored information become exposed.
How to Protect Personal Information From Cyber Threats
Protecting personal information begins with using strong, unique passwords for different online accounts. Reusing the same password across multiple websites increases the risk of several accounts being compromised after one data breach. A reputable password manager can help create and store complex passwords securely. Enabling multifactor authentication adds another layer of account protection.
Keeping devices and applications updated is another practical cybersecurity habit. Software developers regularly release updates that address security weaknesses and improve protection against known vulnerabilities. Automatic updates can make this process easier for everyday users. Installing applications from trusted sources and reviewing requested permissions also helps reduce unnecessary exposure to harmful or intrusive software.
You should also be careful when sharing information through websites, emails, and social media platforms. Avoid entering sensitive details into unfamiliar forms or responding to unexpected messages requesting private information. Check website addresses and verify suspicious requests independently. These simple online safety practices help protect personal data without requiring advanced technical knowledge or expensive security tools.
Cybersecurity Protection Best Practices for Businesses
Businesses should begin by identifying their most valuable digital assets and understanding the risks associated with them. Customer databases, employee records, payment information, and internal systems may require different protection measures. A cybersecurity risk assessment helps identify weaknesses and prioritize improvements. Organizations can then establish security policies that match their operations, resources, and potential threats.
Employee awareness is another essential part of business cybersecurity protection. Staff members may encounter phishing emails, suspicious attachments, or requests for confidential information during normal work activities. Regular training helps employees recognize warning signs and report unusual situations. Clear reporting procedures also make it easier for security teams to investigate potential incidents before problems become more serious.
Businesses should also maintain secure backups, monitor critical systems, and restrict access to sensitive information. Employees should receive only the permissions necessary to perform their responsibilities. Regular security reviews can identify outdated software, unnecessary accounts, and configuration weaknesses. Preparing an incident response plan helps organizations react more effectively when cyber threats affect their systems or information.
The Role of Data Protection and Encryption in Cybersecurity
Data protection focuses on keeping digital information secure, accurate, and available to authorized users. It applies to personal records, business documents, financial details, and other sensitive information. Cybersecurity measures support data protection by preventing unauthorized access and reducing the risk of information loss. Effective data management also includes deciding what information should be collected, retained, and deleted.
Encryption is an important technology for protecting information both during transmission and while stored. For example, encrypted connections help secure data traveling between a browser and a website. Device and storage encryption can also reduce exposure if hardware is lost or stolen. However, encryption cannot prevent every security problem, especially when an attacker gains access to an authorized account.
Access controls and reliable backups provide additional safeguards for important information. Access controls determine who can view, change, or share specific files and systems. Backups create separate copies that may be used to restore information after accidental deletion, technical failures, or certain cyberattacks. Combining these practices supports confidentiality, information accuracy, and business continuity.
How Cybersecurity Protection Helps Prevent Data Breaches
A data breach occurs when sensitive or protected information is accessed, disclosed, or exposed without authorization. Breaches may result from stolen credentials, software vulnerabilities, human mistakes, or malicious attacks. Cybersecurity protection reduces these risks by addressing weaknesses before attackers exploit them. Regular vulnerability assessments and access reviews are useful preventive measures for organizations managing confidential information.
Monitoring and detection systems can also help organizations recognize suspicious behavior. For example, unusual login activity or unexpected attempts to access restricted information may trigger security alerts. Investigating these events quickly can help limit potential damage. However, security alerts require appropriate review because not every unusual activity represents a confirmed cyberattack.
Organizations should also prepare for situations where preventive measures fail. An effective incident response process includes identifying affected systems, containing the problem, and determining what information may have been exposed. Appropriate communication and recovery procedures support a coordinated response. Reviewing the incident afterward helps identify improvements that may reduce the likelihood of similar events.
Understanding the CIA Triad in Cybersecurity Protection
The CIA triad is a fundamental cybersecurity model built around confidentiality, integrity, and availability. These three principles help organizations understand what their security measures should protect. Confidentiality focuses on preventing unauthorized information access, while integrity concerns the accuracy and reliability of information. Availability ensures that authorized users can access essential data and services when needed.
Confidentiality can be supported through encryption, authentication, and appropriate access restrictions. Integrity measures may include file permissions, change tracking, and methods for detecting unauthorized modifications. Availability is supported through backups, reliable infrastructure, and recovery planning. These safeguards work together because strong cybersecurity requires more than simply keeping information secret from unauthorized users.
For example, an online banking service must protect customer details while ensuring transaction records remain accurate. It must also keep essential services accessible to legitimate customers. A failure in any one of these areas can create serious problems. The CIA triad provides a useful foundation for evaluating security priorities across different digital systems.
Cloud Cybersecurity Protection and Remote Work Security
Cloud computing allows businesses to store information and run applications through remotely managed infrastructure. These services offer flexibility, but they also require careful security management. Misconfigured storage, excessive account permissions, and stolen login credentials can create serious risks. Cloud cybersecurity protection addresses these issues through identity management, monitoring, encryption, and secure configuration practices.
Cloud providers and customers typically share responsibility for different security tasks. Providers generally secure the underlying infrastructure, while customers remain responsible for areas such as user access, data settings, and application configuration. The exact responsibilities depend on the service model. Understanding this arrangement helps businesses avoid assuming that all security requirements are automatically handled by the provider.
Remote work introduces additional challenges because employees may access business systems from different devices and networks. Organizations can reduce exposure by using secure authentication, managed devices, and appropriate connection protections. Staff should also understand how to handle business information outside the office. Clear policies and regular security awareness training support safer remote collaboration.
Cybersecurity Protection for Mobile Devices and Online Accounts
Smartphones and tablets contain valuable information, including contacts, photographs, financial applications, and saved account credentials. Their frequent use makes mobile security an important part of cybersecurity protection. Installing operating system updates, enabling screen locks, and using trusted applications are practical safeguards. Device encryption and remote recovery features may provide additional protection if a device is lost.
Mobile users should pay attention to application permissions and unexpected requests for information. Some applications ask for access to contacts, location, cameras, or files that may not be necessary for their functions. Reviewing these permissions helps limit unnecessary data exposure. Avoiding suspicious messages and unfamiliar download links can also reduce the risk of mobile malware and account compromise.
Online account security should extend beyond choosing strong passwords. Authentication apps, passkeys, and other secure sign-in methods can help prevent unauthorized access. Reviewing connected devices and active sessions may reveal unfamiliar account activity. When suspicious access is detected, users should follow the service’s official account recovery and security procedures to regain control safely.
How Artificial Intelligence Is Changing Cybersecurity Protection
Artificial intelligence is increasingly used to support cybersecurity monitoring and threat analysis. AI-based systems can examine large amounts of security data and identify patterns that may indicate unusual activity. This can help security teams prioritize alerts and investigate potential threats more efficiently. However, automated findings still require appropriate evaluation because false alarms and missed threats remain possible.
AI can also assist with identifying suspicious messages, harmful files, and unusual account behavior. Some security platforms use machine learning to recognize patterns that differ from expected activity. These capabilities may improve detection when combined with established security controls. They do not replace basic safeguards such as software updates, access management, and employee awareness training.
Cybercriminals can also misuse AI to create more convincing phishing messages and misleading digital content. This makes verification and security education increasingly important for individuals and organizations. Businesses should evaluate AI security tools carefully, including their accuracy, privacy implications, and operational requirements. Responsible AI adoption can strengthen cybersecurity protection when supported by human oversight and reliable security practices.
Common Cybersecurity Protection Mistakes to Avoid
One common cybersecurity mistake is relying on a single security tool for complete protection. Installing antivirus software does not automatically secure every online account, network connection, or application. Effective protection requires multiple safeguards working together. Combining strong authentication, regular updates, secure backups, and user awareness provides broader coverage against different types of cyber threats.
Another mistake is ignoring software updates or delaying important security fixes. Outdated systems may contain known vulnerabilities that attackers can exploit. Businesses sometimes postpone updates because they worry about service interruptions or compatibility problems. Testing updates when necessary and applying security patches promptly can help balance operational stability with the need for stronger protection.
Failing to prepare for security incidents is another important weakness. Organizations may focus heavily on prevention while overlooking backup testing, recovery procedures, and employee reporting processes. Even well-protected systems can experience security failures. Practicing incident response and reviewing security policies regularly helps teams respond more effectively when unexpected problems occur.
How to Build an Effective Cybersecurity Protection Strategy
An effective cybersecurity strategy begins with understanding what needs protection and which threats are most relevant. Organizations should identify important systems, sensitive information, and potential weaknesses. This assessment helps determine where security resources will provide the greatest benefit. A clear strategy should also consider business size, available technology, regulatory obligations, and operational requirements.
The next step involves selecting appropriate security controls and assigning responsibility for maintaining them. Strong authentication, secure network settings, reliable backups, and regular software updates are useful starting points. Employees should understand relevant security policies and reporting procedures. Organizations can also establish measurable goals to evaluate whether their protection measures are working as intended.
Cybersecurity strategies should be reviewed regularly because technology, business operations, and cyber threats continue changing. New applications, employee accounts, and cloud services may introduce risks that did not previously exist. Periodic assessments help organizations identify these changes and adjust their security measures. Continuous improvement makes cybersecurity protection a practical, ongoing responsibility rather than a one-time project.
Conclusion
Cybersecurity protection involves the tools, practices, and procedures used to keep digital systems and information secure. It helps protect against threats such as malware, phishing, account theft, ransomware, and unauthorized data access. Understanding how these safeguards work is important for anyone who uses internet-connected devices or manages sensitive business information.
Effective cybersecurity requires a combination of preventive measures, monitoring, and recovery planning. Strong passwords, multifactor authentication, security updates, encryption, and reliable backups all contribute to safer digital environments. Businesses can strengthen these protections through employee training, access management, and regular risk assessments.
As digital technology continues evolving, cybersecurity protection remains an ongoing priority. Individuals and organizations should review their security habits and adapt to emerging risks. By applying practical safeguards consistently, they can reduce cyber threats, protect important information, and maintain greater confidence when using digital services.
Frequently Asked Questions (FAQs)
What is cybersecurity protection in simple words?
Cybersecurity protection means keeping computers, online accounts, networks, and digital information safe from cyber threats. It uses security tools and good online habits to reduce unauthorized access, data theft, and system damage.
What are the five main types of cybersecurity protection?
Five common types are network security, endpoint security, application security, cloud security, and data security. Each focuses on protecting different parts of digital systems against unauthorized access and cyber threats.
Why do businesses need cybersecurity protection?
Businesses need cybersecurity protection to secure customer information, prevent operational disruptions, and reduce financial risks. Effective security practices also support customer trust, regulatory compliance, and reliable daily business operations.
What is the difference between cybersecurity and data protection?
Cybersecurity protects digital systems, networks, and information against cyber threats. Data protection focuses more broadly on safeguarding information throughout its lifecycle, including privacy, appropriate access, secure storage, and responsible handling.
How can beginners improve their cybersecurity protection?
Beginners can improve cybersecurity by using unique passwords, enabling multifactor authentication, updating software, and avoiding suspicious links. Regular backups and careful sharing of personal information provide additional protection against common online threats.