
What Are Cybersecurity Operations?
Cybersecurity operations refer to the continuous activities organizations perform to protect their digital systems, networks, applications, and sensitive information from cyber threats. These activities include monitoring suspicious behavior, identifying vulnerabilities, investigating security incidents, and responding to attacks. Unlike occasional security assessments, cybersecurity operations involve ongoing protection and improvement. Their primary purpose is to reduce security risks and maintain reliable business operations.
Modern organizations depend on digital technologies to manage communication, financial transactions, customer information, and everyday business activities. This dependence creates opportunities for cybercriminals to exploit software weaknesses, compromised accounts, and poorly secured systems. Cybersecurity operations help organizations identify potential threats before they cause widespread damage. They also provide structured processes for recovering when security incidents occur.
A successful cybersecurity operations strategy combines skilled professionals, security technologies, and clearly defined procedures. Security analysts examine alerts, investigate unusual activities, and coordinate responses to potential attacks. Automated tools support these efforts by collecting information and identifying suspicious patterns across different systems. Together, these activities establish a coordinated approach to protecting organizational assets.
Why Are Cybersecurity Operations Important?
Cybersecurity operations are essential because digital threats continue to affect organizations of different sizes and industries. Businesses face risks involving phishing, ransomware, unauthorized access, and data breaches. Without consistent monitoring, malicious activities may remain undetected for extended periods. Effective security operations improve visibility into potential threats and help organizations respond before incidents become more damaging.
Protecting sensitive information is another important responsibility of cybersecurity teams. Organizations frequently store customer records, financial documents, employee information, and confidential business data. Unauthorized access to these resources can result in financial losses, regulatory consequences, and damaged customer confidence. Cybersecurity operations reduce these risks through access monitoring, security controls, and incident response procedures.
Operational continuity also depends on maintaining reliable security practices. A successful cyberattack can interrupt business services, prevent employees from accessing important systems, and disrupt customer experiences. Security operations teams work to identify threats quickly and support recovery after incidents. Their efforts help organizations maintain essential services while strengthening protection against future attacks.
How Do Cybersecurity Operations Work?
Cybersecurity operations follow a continuous cycle of monitoring, detection, investigation, response, and improvement. Security tools collect information from networks, servers, endpoints, applications, and cloud environments. Analysts review this information to identify unusual behavior or indicators of compromise. When suspicious activity appears, established procedures help determine whether further investigation or immediate action is necessary.
The process often begins with automated security monitoring systems that generate alerts based on predefined rules and behavioral patterns. Security analysts examine these alerts to distinguish genuine threats from harmless activity. Confirmed incidents are classified according to their severity, potential impact, and affected resources. The response team then follows appropriate procedures to contain threats and reduce business disruption.
After an incident has been addressed, cybersecurity teams review what happened and identify opportunities for improvement. They may update detection rules, strengthen access controls, or recommend additional employee training. Lessons learned from previous incidents help refine security procedures and improve future responses. This continuous improvement process makes cybersecurity operations more effective as organizational environments and threats evolve.
Key Components of Cybersecurity Operations
Security monitoring is one of the fundamental components of cybersecurity operations. It involves continuously observing digital environments for suspicious activity, unauthorized access, and unusual system behavior. Monitoring tools collect logs and security events from connected devices and applications. These records provide valuable information that analysts can use to recognize potential attacks and investigate security concerns.
Threat detection and incident response represent another important component of operational cybersecurity. Detection systems identify activities that may indicate malicious behavior, while response procedures guide teams through investigation and containment. Effective coordination between these functions helps reduce the time attackers remain undetected. It also supports faster recovery when important systems or sensitive information are affected.
Vulnerability management, security configuration, and threat intelligence further strengthen cybersecurity operations. Vulnerability management identifies weaknesses that attackers could exploit, while secure configurations reduce unnecessary exposure. Threat intelligence provides information about emerging attack methods and known malicious activity. Combining these components creates a more comprehensive approach to identifying, preventing, and responding to cybersecurity risks.
What Is a Security Operations Center (SOC)?
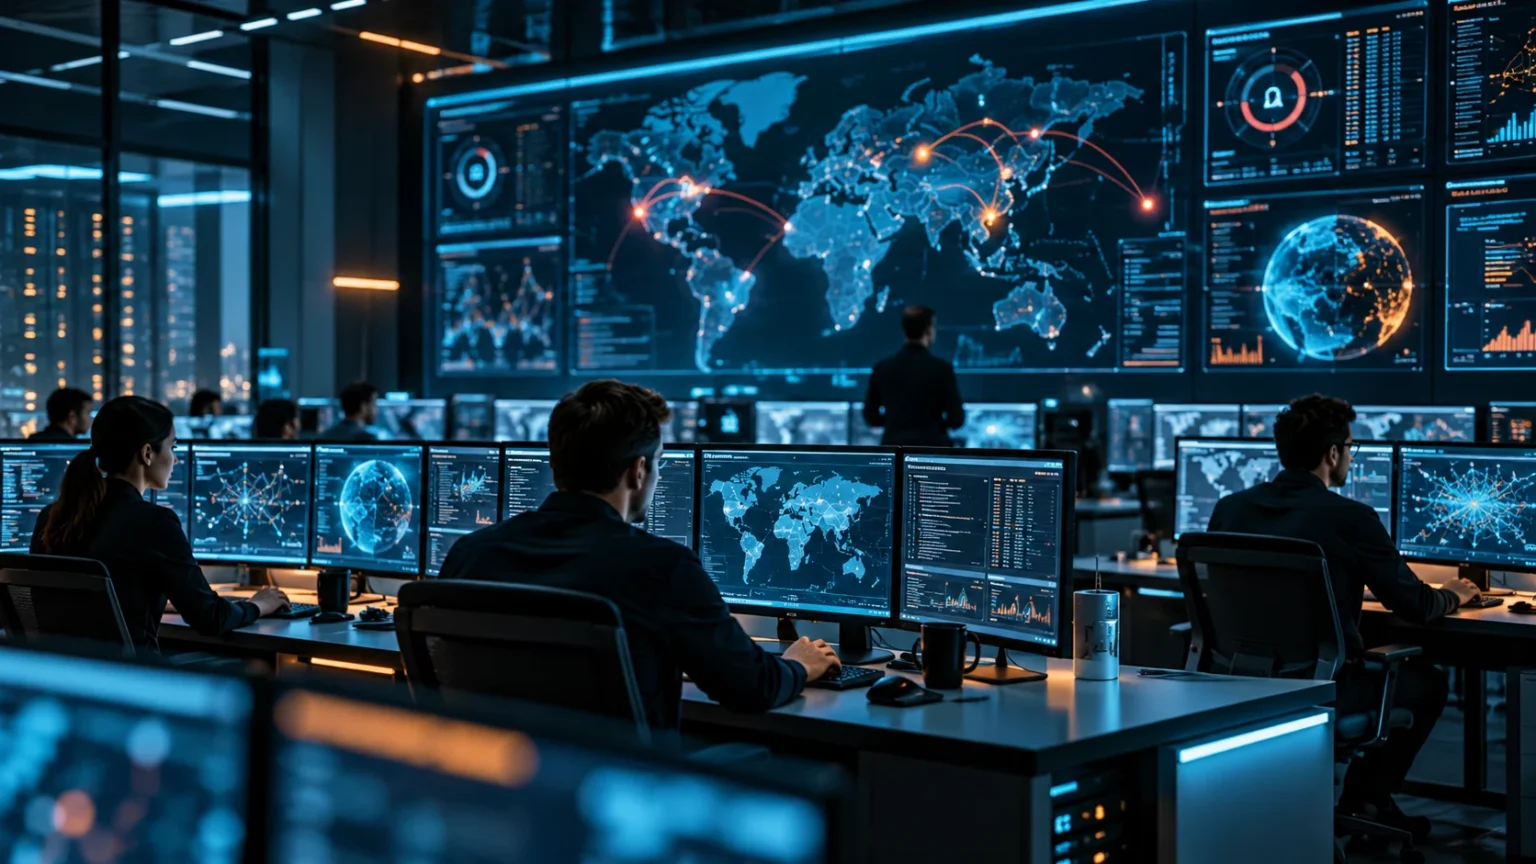
A Security Operations Center, commonly called a SOC, is a centralized function responsible for monitoring and managing an organization’s cybersecurity activities. It may operate through an internal team, an external security provider, or a combination of both. SOC professionals use monitoring platforms and investigation tools to detect potential threats. Their objective is to identify security incidents and coordinate appropriate responses.
A typical security operations center includes security analysts, incident responders, security engineers, and team leaders. Entry-level analysts often review alerts and perform initial investigations, while experienced specialists handle complex incidents. Engineers maintain security monitoring technologies and improve detection capabilities. Clear responsibilities help these professionals collaborate efficiently when suspicious events require attention.
Not every organization needs a large, dedicated physical security operations center. Smaller businesses may use managed security services or cloud-based monitoring solutions to support cybersecurity operations. The most suitable approach depends on organizational size, available resources, and security requirements. Regardless of the structure, effective SOC operations require reliable monitoring, documented procedures, and skilled decision-making.
Threat Detection and Continuous Security Monitoring
Threat detection helps organizations identify potential cyberattacks by examining activity across their digital environments. Security monitoring systems analyze network traffic, login attempts, endpoint behavior, and application events. Suspicious patterns may include unusual account access, unexpected file changes, or communication with known malicious destinations. These indicators can prompt further investigation by cybersecurity professionals.
Continuous monitoring improves the likelihood of identifying threats before they cause extensive damage. Instead of relying entirely on scheduled assessments, security teams examine activity as events occur. Automated alerts help highlight suspicious behavior that requires attention. However, analysts must evaluate these alerts carefully because legitimate business activities can sometimes resemble malicious actions.
Effective threat detection depends on combining technical information with knowledge of normal organizational behavior. Security teams establish monitoring rules, review threat intelligence, and adjust detection methods as systems change. They also examine trends to identify repeated suspicious activities. This approach improves security visibility while helping organizations prioritize incidents that present meaningful risks.
Incident Response and Cybersecurity Incident Management
Incident response is the organized process of investigating and managing confirmed or suspected cybersecurity incidents. It helps organizations limit damage, protect affected systems, and restore normal operations. A documented incident response plan outlines responsibilities, communication procedures, and technical recovery activities. Preparing these processes in advance improves coordination when teams face time-sensitive security situations.
The incident response process commonly includes preparation, identification, containment, eradication, recovery, and lessons learned. During containment, teams work to prevent an incident from spreading to additional systems. Eradication focuses on removing the underlying threat, while recovery restores affected services safely. Each activity requires careful decisions based on the nature and severity of the incident.
Communication is equally important throughout cybersecurity incident management. Technical teams may need to coordinate with management, legal professionals, customer support, and external service providers. Accurate documentation helps organizations understand what happened and determine whether notifications are required. Reviewing completed incidents also strengthens future response procedures and improves organizational readiness.
Essential Tools Used in Cybersecurity Operations
Cybersecurity operations rely on specialized technologies to monitor environments, investigate threats, and coordinate responses. Security Information and Event Management systems, commonly known as SIEM platforms, collect and analyze security-related data from multiple sources. They help analysts identify suspicious patterns and investigate security alerts. Centralized visibility makes it easier to understand events occurring across an organization’s infrastructure.
Endpoint Detection and Response tools, or EDR solutions, focus on identifying suspicious behavior on computers and other supported devices. Extended Detection and Response platforms, known as XDR, combine information from multiple security areas to improve investigations. These technologies help security teams understand potential threats across connected systems. Their usefulness depends on appropriate configuration, monitoring coverage, and analyst expertise.
Security Orchestration, Automation, and Response platforms, commonly called SOAR tools, help streamline repetitive security workflows. They may automatically enrich alerts, organize incident information, or initiate approved response procedures. Vulnerability scanners and threat intelligence platforms provide additional information for risk management. Organizations should select technologies based on their security requirements rather than simply purchasing more tools.
The Role of Cyber Threat Intelligence
Cyber threat intelligence involves collecting and analyzing information about potential attackers, attack methods, and emerging security risks. It helps cybersecurity teams understand which threats may be relevant to their organization. Intelligence sources can include security research, internal investigations, and information-sharing communities. This knowledge supports better decisions about security monitoring, vulnerability priorities, and defensive measures.
Threat intelligence becomes particularly valuable when connected to operational security processes. Analysts can compare suspicious activities against known indicators of compromise or common attacker techniques. This comparison provides additional context during investigations and helps prioritize relevant alerts. However, intelligence indicators must be evaluated carefully because threats and attacker infrastructure change over time.
Organizations can also use threat intelligence to support longer-term cybersecurity planning. Understanding common attack patterns may reveal areas where additional protection or employee awareness is needed. Security teams can refine monitoring rules and strengthen vulnerable systems based on relevant findings. Effective intelligence programs focus on actionable information rather than collecting large amounts of unrelated threat data.
Vulnerability Management and Risk Assessment
Vulnerability management is an ongoing process for identifying, evaluating, and addressing weaknesses in digital systems. Software defects, outdated applications, and insecure configurations can create opportunities for unauthorized access. Security teams use scanning technologies and assessments to discover potential weaknesses. Identifying these issues early allows organizations to reduce exposure before attackers exploit them.
Not every vulnerability presents the same level of risk to an organization. Teams consider factors such as exploitability, affected systems, available protections, and business importance when determining priorities. A serious weakness in an internet-facing service may require faster attention than a less accessible issue. Risk-based prioritization helps organizations allocate limited security resources effectively.
Remediation activities may include installing security updates, changing system configurations, or restricting unnecessary access. When immediate fixes are unavailable, temporary protective measures can help reduce risk. Security teams should verify whether corrective actions successfully addressed the identified weaknesses. Regular reassessment ensures that vulnerability management remains relevant as technologies and business requirements change.
Cybersecurity Operations in Cloud and Hybrid Environments
Cloud computing has expanded the responsibilities of cybersecurity operations teams. Organizations increasingly use cloud applications, hosted infrastructure, and remote collaboration platforms to support daily work. These environments introduce security considerations involving identity management, configuration, data access, and monitoring. Cybersecurity teams must understand how cloud technologies operate to protect information stored across different platforms.
Cloud security often follows a shared responsibility model between service providers and their customers. Providers generally secure certain underlying infrastructure components, while customers remain responsible for specific configurations, identities, applications, and data protections. Exact responsibilities vary according to the service model. Security operations teams must understand these boundaries to avoid overlooking important controls.
Hybrid environments introduce additional complexity because they combine on-premises infrastructure with cloud services. Security teams need consistent visibility across networks, endpoints, user accounts, and connected applications. Centralized monitoring and well-defined access policies can help reduce gaps between environments. Effective cloud cybersecurity operations require adapting security procedures as infrastructure and business requirements evolve.
The Role of Automation and Artificial Intelligence
Automation helps cybersecurity teams manage repetitive activities that would otherwise require significant manual effort. Security systems can collect logs, organize alerts, and enrich incident information automatically. These capabilities allow analysts to spend more time investigating complex threats and improving protective measures. Well-designed automation can also support consistent responses to common security events.
Artificial intelligence and machine learning can assist with identifying unusual patterns in large volumes of security data. Some tools analyze behavior to detect activities that traditional security rules might overlook. AI-assisted systems may also help summarize incidents or support investigation workflows. However, their findings require validation because automated systems can generate inaccurate conclusions or overlook important context.
Organizations should introduce automation carefully, particularly when workflows can affect critical systems or user access. Incorrectly configured responses may interrupt legitimate business activities. Human oversight, testing, and clear approval procedures help reduce these risks. Automation is most effective when it supports experienced security professionals rather than replacing informed judgment and accountability.
Cybersecurity Operations vs. Cybersecurity Management
Cybersecurity operations and cybersecurity management are closely related, but they focus on different responsibilities. Security operations concentrate on monitoring systems, investigating threats, and responding to active incidents. Cybersecurity management addresses broader planning, policies, budgets, governance, and organizational risk. Both functions contribute to protecting digital assets, but they operate at different levels.
For example, cybersecurity management may establish security objectives and approve an organization’s incident response policy. Security operations teams then apply those requirements through monitoring procedures, technical controls, and investigations. Operational findings can reveal weaknesses that require management decisions or additional investment. This connection helps organizations align daily security activities with broader business priorities.
Effective cybersecurity programs require ongoing communication between operational teams and organizational leadership. Managers need reliable information about security incidents, vulnerabilities, and performance to make informed decisions. Security professionals need clear priorities and sufficient resources to carry out their responsibilities. When these functions work together, organizations can make more consistent improvements to their security posture.
Cybersecurity Operations Best Practices for Businesses
Establishing clear security responsibilities is an important starting point for effective cybersecurity operations. Organizations should document monitoring procedures, incident response plans, and escalation requirements. Employees need to understand how to report suspicious activity and who handles security concerns. Regular reviews help ensure that these procedures remain useful as business systems and staffing arrangements change.
Businesses should also prioritize strong identity protection and access management. Multifactor authentication, appropriate user permissions, and timely account reviews can reduce opportunities for unauthorized access. Consistent software updates and secure system configurations provide additional protection. These foundational measures support operational monitoring by reducing preventable security weaknesses across the organization.
Regular security exercises and performance reviews help organizations evaluate their readiness. Incident response simulations can reveal communication problems, unclear responsibilities, or gaps in technical procedures. Teams should measure outcomes such as detection coverage, response effectiveness, and remediation progress. Continuous improvement makes cybersecurity operations more reliable and better aligned with changing business risks.
Common Challenges in Cybersecurity Operations
One major challenge in cybersecurity operations is managing the large volume of security alerts generated by modern monitoring systems. Analysts may encounter numerous notifications that do not represent genuine threats. Excessive alert volumes can slow investigations and make important incidents harder to identify. Improving detection quality and establishing clear priorities can help reduce this operational burden.
A shortage of experienced cybersecurity professionals can also affect security operations teams. Organizations may struggle to recruit specialists with knowledge of threat analysis, incident response, and cloud security. Smaller businesses often face additional budget and staffing limitations. Training employees, improving workflows, and considering appropriate managed security services can help address some of these challenges.
Rapid technological change creates further difficulties because security teams must protect constantly evolving systems. New applications, cloud services, and remote work arrangements can expand the potential attack surface. Attackers also adapt their techniques to exploit emerging weaknesses. Maintaining accurate asset inventories, updating monitoring capabilities, and reviewing security practices regularly are essential for managing these risks.
Career Opportunities in Cybersecurity Operations
Cybersecurity operations offer several career paths for people interested in protecting digital systems. Common positions include SOC analyst, cybersecurity analyst, incident responder, threat intelligence analyst, and security engineer. These professionals perform different tasks, ranging from monitoring alerts to investigating complex security incidents. Understanding the responsibilities of each role can help beginners identify suitable career directions.
Entry-level professionals often begin by learning networking fundamentals, operating systems, security concepts, and basic log analysis. Practical experience with monitoring platforms and investigation procedures can support skill development. Training programs, hands-on laboratories, and relevant certifications may help demonstrate foundational knowledge. Communication and analytical thinking are equally valuable because security investigations frequently involve collaboration and documentation.
As professionals gain experience, they may specialize in incident response, threat hunting, detection engineering, or security operations leadership. Advanced roles often require deeper technical knowledge and the ability to manage complex security situations. Continued learning is important because technologies and attack techniques change regularly. A cybersecurity operations career can provide opportunities to develop both technical and organizational expertise.
Conclusion
Cybersecurity operations play a central role in protecting organizations from digital threats and maintaining reliable business services. Through continuous monitoring, threat detection, incident response, and vulnerability management, security teams reduce exposure to cyber risks. These activities help organizations identify suspicious behavior and respond to incidents more effectively. A coordinated approach provides stronger protection than relying on isolated security tools.
Successful cybersecurity operations depend on the combination of technology, skilled professionals, and well-defined processes. Security operations centers, threat intelligence, automation, and risk assessments support informed defensive decisions. Regular testing and improvement help organizations adapt to changing technologies and emerging threats. Clear communication between security teams and business leadership further strengthens operational effectiveness.
As organizations expand their digital environments, cybersecurity operations will remain an important business responsibility. Investing in appropriate security capabilities can support data protection, operational continuity, and customer confidence. Businesses of every size can benefit from practical monitoring and response procedures suited to their needs. Building consistent security practices today helps organizations prepare for future cybersecurity challenges.
Frequently Asked Questions (FAQs)
What is the main purpose of cybersecurity operations?
The main purpose of cybersecurity operations is to protect digital systems and information through continuous monitoring, threat detection, investigation, and incident response. These activities reduce security risks and support business continuity.
What is the difference between cybersecurity and cybersecurity operations?
Cybersecurity is the broader practice of protecting digital assets, while cybersecurity operations focus on the ongoing activities used to detect, investigate, and respond to threats within an organization.
What does a cybersecurity operations analyst do?
A cybersecurity operations analyst monitors security alerts, investigates suspicious activities, reviews system logs, and helps respond to incidents. Analysts also document findings and recommend improvements to security controls.
What tools are commonly used in cybersecurity operations?
Common tools include SIEM platforms, EDR solutions, XDR systems, SOAR platforms, vulnerability scanners, and threat intelligence services. These technologies support monitoring, investigations, risk assessment, and incident response.
Is cybersecurity operations a good career?
Cybersecurity operations can be a rewarding career for individuals interested in technology, investigation, and digital security. Career opportunities include SOC analysis, incident response, threat hunting, and security engineering.