
Cybersecurity is essential for protecting digital systems, networks, and sensitive information from online threats. However, understanding how different security technologies work together can be challenging, especially for beginners. A cybersecurity diagram helps simplify this process by presenting complex security structures in a clear visual format.
Organizations use cybersecurity diagrams to understand network connections, identify potential vulnerabilities, and explain how security controls protect important systems. These diagrams can illustrate firewalls, servers, data flows, authentication processes, and possible cyberattack paths. Understanding how they work is useful for IT professionals, cybersecurity students, business owners and anyone interested in digital security.
What Is a Cybersecurity Diagram?
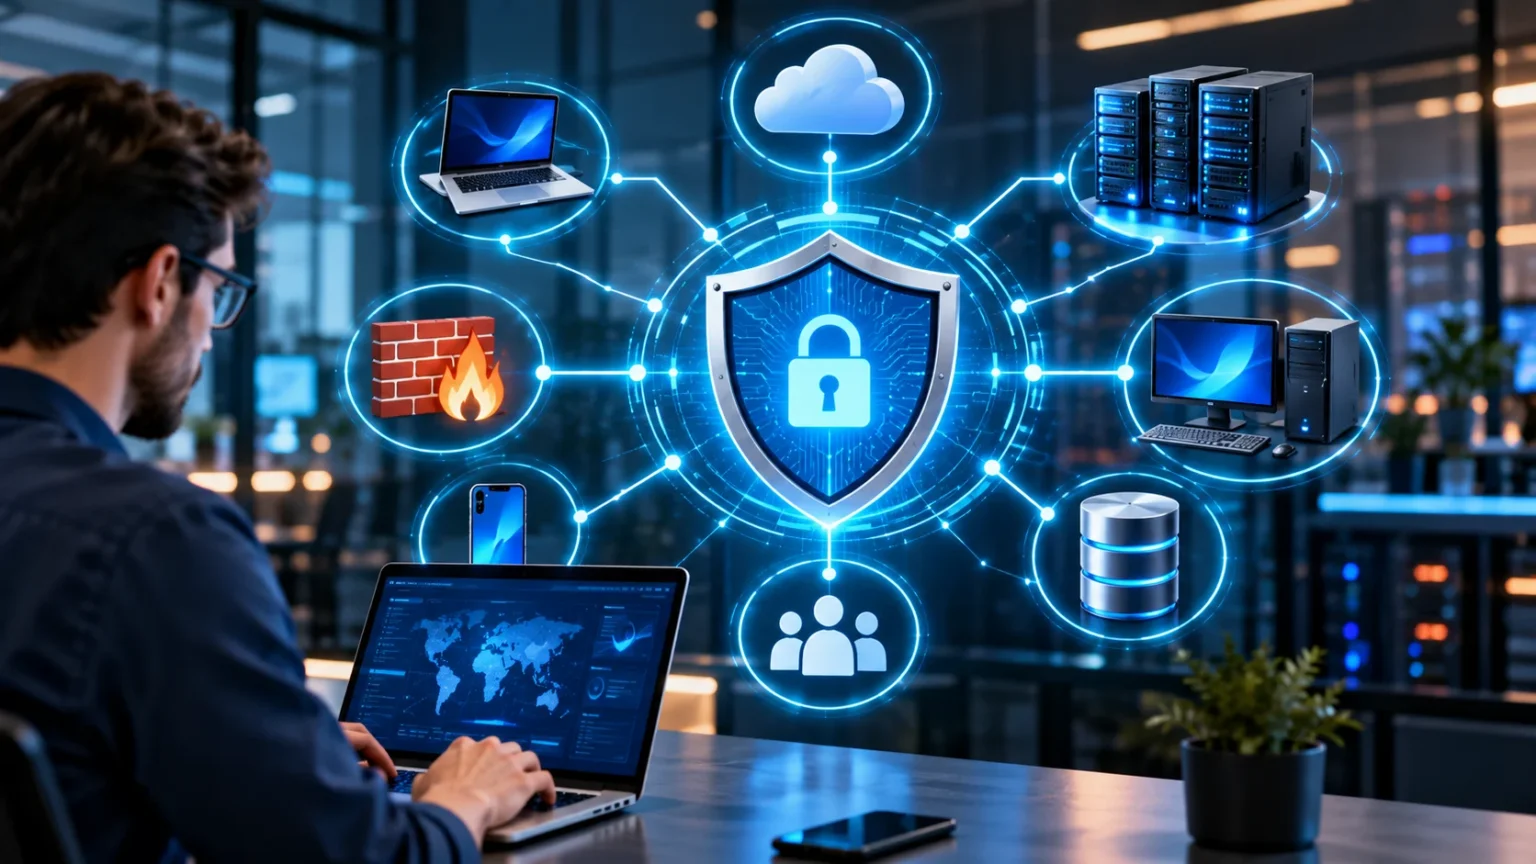
A cybersecurity diagram is a visual representation of the systems, technologies, and processes used to protect digital information. It shows how different components connect and interact within a network or security environment. These components may include firewalls, servers, computers, cloud services, and security monitoring tools. The diagram helps people understand how cybersecurity measures work together to protect important digital resources.
Instead of describing security infrastructure through lengthy technical explanations, a cybersecurity diagram uses symbols, shapes, and connecting lines. Each element represents a particular device, system, security control, or communication process. Arrows can show the direction of data movement, while boundaries identify separate network environments. This visual approach makes complex cybersecurity architecture easier to understand and discuss.
Cybersecurity diagrams are useful for both small businesses and large organizations. A small company might create a simple network security diagram showing its router, firewall, and connected computers. A large enterprise may require detailed diagrams covering multiple offices, cloud platforms, and security systems. The complexity depends on the organization’s infrastructure and the information the diagram needs to communicate.
Why Are Cybersecurity Diagrams Important?
Cybersecurity diagrams help organizations develop a clearer understanding of their digital security infrastructure. When security components are displayed visually, IT teams can identify how systems communicate and where protective measures operate. This understanding supports better security planning and infrastructure management. It also helps organizations recognize areas that may require additional monitoring, maintenance, or protection.
Another important benefit is improved communication between technical and nontechnical teams. Cybersecurity professionals often need to explain security risks and technical decisions to business managers or other stakeholders. A well-designed diagram can make these discussions easier by showing important relationships visually. Instead of relying entirely on technical language, teams can use the diagram to explain how systems are protected.
Cybersecurity diagrams also support incident response and security assessments. During a security investigation, teams may need to identify affected systems and understand how information moves through the network. An accurate diagram can help them locate relevant connections and security controls more efficiently. However, diagrams should support technical investigation rather than replace monitoring systems, configuration reviews, or other security evidence.
Essential Components of a Cybersecurity Diagram
Most cybersecurity diagrams contain several important elements that explain how a protected environment operates. Common components include network devices, servers, endpoints, databases, and security appliances. Each component is usually represented by a recognizable symbol or labeled shape. Together, these elements provide a visual overview of the organization’s infrastructure and the resources that require protection.
Security controls are another essential part of cybersecurity architecture diagrams. Firewalls, intrusion detection systems, endpoint protection tools, and identity management services may appear within the design. Their placement helps viewers understand which systems they protect and where security inspection occurs. Including these controls also makes it easier to identify important protection layers and potential gaps.
Connections and boundaries provide additional context within a cybersecurity diagram. Lines represent communication paths, while arrows may indicate the direction of data movement. Network zones can separate public services, internal systems, and restricted environments. Trust boundaries identify locations where information crosses between areas with different security requirements, helping teams understand where additional verification or protection may be necessary.
Different Types of Cybersecurity Diagrams
Network security diagrams are among the most common visual tools used in cybersecurity. They show how computers, routers, switches, servers, and security devices connect within a network. These diagrams may also illustrate internet connections, virtual private networks, and network segmentation. Security teams use them to understand network structure, review communication paths, and identify areas where defensive controls should operate.
Data flow diagrams focus on how information moves between users, applications, databases, and external services. They help organizations understand where sensitive information enters, travels through, and leaves a system. This information is useful when evaluating privacy risks, data protection requirements, and possible exposure points. Data flow diagrams are especially relevant when applications process confidential business information or customer records.
Other common examples include security architecture diagrams, threat modeling diagrams, and identity access diagrams. Security architecture diagrams present the overall defensive design of a system or organization. Threat modeling diagrams help teams examine how weaknesses might be exploited, while identity diagrams explain authentication and authorization relationships. Each type serves a different purpose, so organizations often maintain several diagrams.
How Does a Network Security Diagram Work?
A network security diagram illustrates how devices and security technologies communicate within an organization’s network. It usually begins with external connections, such as the internet, and shows how traffic reaches internal services. Firewalls, routers, switches, and servers are arranged according to their roles. This structure helps viewers understand the general path that information follows during network communication.
For example, a business may place a firewall between its internet connection and internal network. The diagram can show internet traffic passing through that firewall before reaching approved services. Additional controls might protect internal servers, employee devices, and sensitive databases. By displaying these relationships, the diagram helps explain how multiple security measures contribute to network protection.
Network security diagrams can also represent segmented environments with different access requirements. Guest wireless networks, employee networks, and restricted server environments may appear as separate zones. Their connections can show where access restrictions or monitoring controls apply. This makes the diagram useful when reviewing network segmentation, identifying unnecessary connections, and planning infrastructure improvements.
Understanding Data Flow and Trust Boundaries
Data flow is an important concept in cybersecurity because information constantly travels between connected systems. A data flow diagram shows where information originates, how it is processed, and where it eventually goes. For example, an online application might receive information from a user and send it to a database. Visualizing this process helps teams identify important data handling activities.
Trust boundaries show where information moves between systems or areas with different levels of trust. A public website communicating with a protected internal service may cross one such boundary. Security controls at that point might include authentication, authorization, input validation, and encrypted communication. Highlighting these boundaries helps cybersecurity teams determine where security requirements should be carefully examined.
Data flow diagrams can also support the protection of sensitive customer and business information. Teams may use them to identify where personal data is collected, stored, shared, or transferred. This visibility helps organizations review encryption, access controls, and data retention practices. Keeping diagrams accurate is important because undocumented data flows can complicate security assessments and privacy reviews.
How Cybersecurity Diagrams Support Threat Modeling
Threat modeling is a structured process for identifying potential security threats before they cause problems. Cybersecurity diagrams provide a useful starting point by showing important systems, communication paths, and trust boundaries. Teams can examine these elements to understand where attackers might attempt unauthorized access. This allows organizations to evaluate potential risks while planning or improving their security architecture.
A threat modeling diagram may identify sensitive assets, external entry points, and connections between applications. Security professionals can use this information to consider risks such as unauthorized access, data exposure, or misuse of system permissions. Each identified threat can then be evaluated according to its likelihood and potential impact. This supports a more organized approach to prioritizing security improvements.
Threat modeling diagrams are especially valuable during application development and infrastructure changes. When teams introduce new services or integrations, the existing security design may change. Updating the diagram helps them understand how additional components affect the overall environment. Reviewing these changes early can reveal potential security weaknesses before the new functionality becomes widely available.
Identity and Access Management in Cybersecurity Diagrams
Identity and access management, commonly called IAM, controls how users and services access digital resources. An IAM cybersecurity diagram shows the relationships between identities, authentication systems, applications, and protected data. It may include employees, administrators, service accounts, and external users. These visual relationships help organizations understand how access decisions are made across their environment.
Authentication and authorization serve different purposes within an identity management system. Authentication verifies that a user or service is who it claims to be, while authorization determines what actions are permitted. A diagram can show authentication services, multifactor authentication, roles, and access policies. Presenting these elements visually makes it easier to understand the organization’s access control process.
IAM diagrams are also useful when reviewing the principle of least privilege. This security practice aims to give users and services only the access necessary for their responsibilities. By mapping roles and permissions, teams can identify relationships that require further investigation. The diagram provides a helpful overview, although detailed permission audits are still needed to confirm actual access rights.
Cybersecurity Diagrams for Cloud and Hybrid Environments
Cloud computing introduces additional components that traditional network diagrams may not fully represent. A cloud cybersecurity diagram can show virtual networks, applications, databases, storage services, and security controls hosted by a cloud provider. It may also illustrate how cloud resources connect to users and external systems. This helps teams understand the architecture of their cloud environment.
Hybrid environments combine on-premises infrastructure with cloud-based services. Their cybersecurity diagrams often include local servers, cloud platforms, private connections, and remote access services. These designs help organizations visualize how information travels between different environments. Clear documentation is particularly useful when multiple teams manage separate portions of the infrastructure or share security responsibilities.
Cloud security diagrams should also reflect important configuration and access relationships. Identity policies, encryption services, logging systems, and network restrictions may all be relevant to the design. Organizations should distinguish between provider-managed protections and security responsibilities they manage themselves. This helps avoid incorrect assumptions about which party is responsible for securing particular resources or configurations.
How to Create a Cybersecurity Diagram Step by Step
Creating a cybersecurity diagram begins with defining its purpose and intended audience. Determine whether the diagram should explain network infrastructure, application security, data movement, or another specific topic. Next, identify the systems, devices, and security controls that belong within its scope. Starting with a clear objective prevents the diagram from becoming unnecessarily complicated or difficult to understand.
After identifying the relevant components, arrange them according to their actual relationships. Place connected systems together and use lines or arrows to represent communication paths. Add labels for important devices, network zones, trust boundaries, and security controls. Diagramming tools such as Microsoft Visio, diagrams.net, or Lucidchart can help organize the design into a readable visual layout.
Once the initial diagram is complete, review it with people who understand the environment. Confirm that important systems, connections, and security controls are represented accurately. Remove unnecessary detail that distracts from the diagram’s main purpose while retaining essential information. Finally, establish a review process so the diagram can be updated when infrastructure or security requirements change.
Best Practices and Common Mistakes to Avoid
An effective cybersecurity diagram should be clear, accurate, and easy to interpret. Use consistent symbols, meaningful labels, and a logical arrangement of components throughout the design. Group related systems together and distinguish different security zones where appropriate. Avoid adding every technical detail to a single diagram, because excessive information can make important relationships harder to recognize.
One common mistake is relying on outdated diagrams after infrastructure changes. New cloud services, applications, network connections, and security tools can change how an environment operates. If these changes are not documented, the diagram may provide an inaccurate understanding of existing protections. Regular reviews and clear ownership help organizations maintain more reliable and useful security documentation.
Another mistake is treating a cybersecurity diagram as proof that an environment is secure. A diagram can illustrate intended protections, but it cannot confirm that controls are configured or operating correctly. Organizations still need vulnerability assessments, monitoring, access reviews, and other security verification activities. Detailed diagrams should also be stored securely because they may reveal sensitive infrastructure information.
Conclusion
A cybersecurity diagram is a valuable tool for understanding how digital systems, networks, and security controls work together. It transforms complex technical relationships into a visual format that is easier to explain and analyze. From network infrastructure to cloud architecture, these diagrams help organizations document important components and understand potential security risks.
Different cybersecurity diagrams serve different purposes, including mapping network connections, visualizing data flows, and supporting threat modeling. Choosing the appropriate type depends on what information needs to be communicated. Accurate labels, clear boundaries, and consistent symbols make the results more useful for both technical teams and business stakeholders.
Learning how to create and interpret cybersecurity diagrams is a practical skill for anyone interested in digital security. Start with a simple system, identify its important components, and gradually develop a more detailed understanding of its connections. Remember that diagrams are most effective when they remain accurate and support broader cybersecurity planning, monitoring, and assessment activities.
Frequently Asked Questions (FAQs)
What is a cybersecurity diagram in simple words?
A cybersecurity diagram is a visual drawing that shows how computer systems, networks, and security tools connect. It helps people understand how digital information is protected and where security controls operate.
What is the main purpose of a cybersecurity diagram?
The main purpose is to explain security infrastructure clearly and visually. It helps organizations understand system connections, review protective measures, identify potential risks, and communicate cybersecurity designs more effectively.
What are the most common types of cybersecurity diagrams?
Common types include network security diagrams, data flow diagrams, security architecture diagrams, threat modeling diagrams, and identity access diagrams. Each type illustrates a different aspect of cybersecurity infrastructure or protection.
Which tools can be used to create cybersecurity diagrams?
Popular diagramming tools include Microsoft Visio, Lucidchart, and diagrams.net. These applications provide shapes, connectors, and layout features that help users create organized visual representations of networks and security architectures.
Can cybersecurity diagrams help prevent cyberattacks?
Cybersecurity diagrams can support prevention by helping teams identify possible weaknesses and understand security coverage. However, diagrams alone cannot stop attacks; organizations must also implement, test, monitor, and maintain effective security controls.