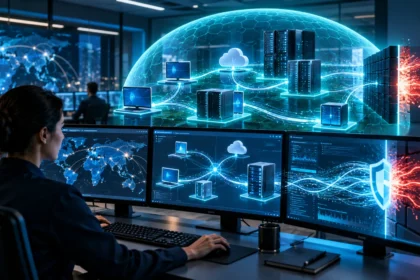

SAP cyber security involves protecting SAP applications, databases, networks, and integrated business systems against cybersecurity threats. It combines identity management, access controls, vulnerability assessments, encryption, security monitoring, and regular system updates. Organizations use these protective measures to reduce security risks while maintaining the availability and reliability of their enterprise applications.
As businesses adopt cloud computing, digital transformation, and interconnected software platforms, securing SAP environments has become increasingly important. A single security weakness can affect multiple business processes and expose confidential information. This guide explains how SAP cyber security works, its major components, common threats, essential security practices, and strategies organizations can use to strengthen enterprise protection.
What Is SAP Cyber Security?
SAP cyber security refers to the technologies, policies, and security practices used to protect enterprise systems developed by SAP. SAP stands for Systems, Applications, and Products in Data Processing, and its software supports essential business processes across organizations. Cybersecurity measures help protect these applications against unauthorized access, data breaches, malware, and other digital threats.
Unlike general cybersecurity, SAP cyber security focuses on protecting complex enterprise environments where multiple applications share sensitive information. These environments often include financial management, human resources, purchasing, inventory, and customer data. Security professionals must understand how SAP applications interact with business processes to identify potential weaknesses. Effective protection requires both technical security controls and proper access management.
SAP security and SAP cybersecurity are closely related but have slightly different areas of emphasis. Traditional SAP security often focuses on user roles, permissions, and authorization management, while SAP cybersecurity covers broader threats involving infrastructure, applications, and connected systems. Both approaches work together to support data confidentiality, system integrity, and operational availability. A comprehensive strategy includes elements of each.
Why Is SAP Cyber Security Important for Businesses?
SAP platforms frequently support critical operations, including financial reporting, payroll processing, procurement, and manufacturing management. Unauthorized access or system disruption can affect several business departments simultaneously. A successful cyberattack may expose confidential information, interrupt business activities, or create financial losses. Strong SAP cybersecurity controls help organizations reduce these risks and maintain reliable operations.
Data protection is another major reason businesses invest in SAP security solutions. Enterprise applications may contain personal information, financial records, supplier contracts, and confidential business strategies. Protecting this information requires appropriate permissions, secure communication, and continuous monitoring. Weak security configurations can expose sensitive data even when the underlying software includes built-in protection features.
Regulatory requirements also influence enterprise security planning. Depending on their industry and location, organizations may need to satisfy privacy, financial reporting, or information security obligations. SAP security controls can support these requirements through access restrictions, activity logging, and documented security procedures. Maintaining effective safeguards can strengthen customer trust and demonstrate responsible handling of business information.
Which SAP Systems Need Cyber Security Protection?
SAP S/4HANA is an enterprise resource planning platform used to manage business operations through integrated applications. Because it processes financial, operational, and organizational information, it requires carefully managed security controls. Organizations should protect user identities, business roles, application configurations, and connections with other systems. Security requirements may differ depending on whether the system operates in the cloud or on premises.
SAP ERP Central Component, commonly called SAP ECC, remains part of some organizations’ technology environments. These systems may contain years of historical business information and connections with external applications. Older configurations, unsupported components, and delayed security updates can increase exposure to cyber threats. Organizations maintaining legacy environments should review their security posture and plan appropriate modernization activities.
Other SAP technologies also require protection, including SAP HANA databases, SAP Business Technology Platform, and cloud applications such as SAP SuccessFactors and SAP Ariba solutions. Each service has different technical characteristics and security responsibilities. Protecting the entire SAP landscape involves understanding how applications exchange information. Security teams must evaluate individual systems and the connections between them.
What Are the Most Common SAP Cyber Security Threats?
Unauthorized access is a significant SAP security concern because enterprise systems contain valuable business information. Attackers may attempt to misuse stolen credentials, compromised accounts, or excessive user privileges. Weak authentication practices and poorly managed permissions can increase exposure. Organizations can reduce these risks through strong identity verification, restricted access, and regular reviews of user accounts.
Unpatched software vulnerabilities represent another important cybersecurity threat. SAP applications, supporting infrastructure, and connected components may contain weaknesses that require security updates. Delaying relevant patches can leave systems exposed to known risks. Misconfigured services, insecure integrations, and unnecessary network access may create additional opportunities for unauthorized activity, particularly in complex environments.
Phishing, ransomware, malicious software, and insider misuse can also affect SAP environments. Employees may receive deceptive messages designed to compromise account credentials, while compromised connected systems can introduce broader security risks. Not every incident originates within SAP software itself. Effective defense requires employee awareness, endpoint protection, secure configurations, and monitoring across the surrounding technology infrastructure.
How Does SAP Identity and Access Management Work?
Identity and access management determines who can enter SAP systems and what actions they are permitted to perform. Administrators assign permissions according to job responsibilities, business requirements, and organizational security policies. Role-based access control helps users perform necessary activities without receiving unrestricted privileges. This approach supports accountability and reduces the potential damage associated with compromised accounts.
SAP authorization concepts use roles and authorization objects to control access to specific functions and information. In SAP environments based on ABAP technology, administrators can manage roles through appropriate administration tools. Permissions should reflect actual business responsibilities rather than convenience. Applying the principle of least privilege helps prevent employees and service accounts from accessing information they do not need.
Strong authentication adds another layer of protection to enterprise access management. Multi-factor authentication, secure identity integration, and appropriate session controls can reduce the risk of unauthorized access. Organizations should also review inactive accounts, privileged users, and access changes when employees change roles. Segregation of duties helps prevent one individual from controlling conflicting activities within sensitive business processes.
How Do SAP Security Notes and Patching Reduce Risk?
SAP Security Notes provide information about identified security vulnerabilities and recommended corrections for affected SAP products. These notices help administrators understand potential weaknesses and determine whether particular systems require attention. Applying relevant corrections is an important part of SAP vulnerability management. However, security teams must consider product versions, dependencies, and implementation requirements before making changes.
SAP regularly publishes security updates, including announcements associated with its monthly Security Patch Day. Organizations should establish processes for reviewing applicable notices and prioritizing important fixes. Highly exposed or business-critical systems may require faster remediation based on their actual risk. A consistent patch management process helps prevent known vulnerabilities from remaining unresolved unnecessarily.
Testing is essential because SAP applications often support tightly connected business operations. Before applying changes to production environments, administrators should assess compatibility and test relevant business processes in appropriate nonproduction systems. Maintenance planning, backups, and rollback procedures can reduce operational disruption. Following implementation, teams should confirm that security corrections are effective and that important functions remain available.
How Does SAP Protect Sensitive Data and Integrations?
Data protection is a central component of SAP cyber security because enterprise applications handle confidential business records. Encryption can help protect information while it travels between systems and, where supported and configured, while it is stored. Access restrictions help prevent unauthorized viewing or modification. Organizations should select appropriate safeguards based on data sensitivity and regulatory requirements.
SAP environments frequently exchange information with external applications through APIs, Remote Function Calls, and other integration technologies. These connections may support payment processing, supplier management, reporting, or customer services. Weakly protected interfaces can introduce security risks beyond the primary SAP application. Authentication, encrypted communication, restricted permissions, and secure credential management help protect information exchanged between connected platforms.
Data security also depends on retention policies, backup protection, and monitoring of sensitive information access. Organizations should identify important data assets and determine who genuinely needs access to them. Secure backups support recovery following incidents or system failures, while appropriate logging improves accountability. Regular reviews help ensure protective measures remain suitable as business processes change.
What Is SAP Cloud Security and Shared Responsibility?
SAP cloud security focuses on protecting enterprise applications, services, identities, and information hosted in cloud environments. Cloud-based SAP solutions can provide flexibility and reduce certain infrastructure management responsibilities. However, moving applications to the cloud does not eliminate cybersecurity risks. Organizations must still manage relevant configurations, user access, integrations, and data protection responsibilities.
The shared responsibility model explains how security duties are divided between a cloud provider and its customers. SAP may manage specific infrastructure or platform security functions, depending on the service being used. Customers remain responsible for certain activities, such as business permissions, user management, and secure application usage. Exact responsibilities depend on the product, service agreement, and deployment model.
SAP Business Technology Platform supports application development, integration, data management, and other enterprise capabilities. Securing SAP BTP environments requires attention to identities, application permissions, connectivity, and security configurations. Organizations using hybrid environments must also protect communication between cloud and on-premises systems. A coordinated approach helps prevent security gaps across different hosting models and connected services.
How Do SAP Security Monitoring and Incident Response Work?
Security monitoring helps organizations identify unusual activities and investigate potential threats within SAP environments. Depending on the product and configuration, security logs can record events such as unsuccessful login attempts, administrative changes, and sensitive system activities. Reviewing these events provides information about possible security concerns. Monitoring becomes more effective when organizations establish clear expectations for normal behavior.
Security information and event management systems, commonly called SIEM platforms, can collect and analyze security information from multiple sources. Integrating relevant SAP logs with broader security monitoring helps analysts investigate suspicious activity across connected applications. Automated alerts can highlight events requiring attention. However, alerts need appropriate configuration and regular review to reduce unnecessary notifications.
Incident response planning defines how an organization should handle suspected cybersecurity events. Teams should establish responsibilities for investigation, containment, recovery, and communication before an incident occurs. Protecting evidence and understanding affected business processes are important considerations during response activities. After an incident, reviewing its causes and improving security controls can reduce the likelihood of similar problems.
What Are the Best Practices for SAP Cyber Security?
Effective SAP cyber security begins with a clear understanding of the systems, users, and information requiring protection. Organizations should maintain an updated inventory of SAP applications, connected services, and important data assets. Regular security assessments can identify outdated configurations and unnecessary access permissions. A risk-based approach helps security teams prioritize weaknesses according to their potential business impact.
Organizations should combine strong authentication, least-privilege permissions, patch management, and secure system configurations. Administrative accounts deserve additional protection because they may have access to sensitive functions. Employees should receive practical security awareness training relevant to their responsibilities. These measures work best when incorporated into everyday operational processes rather than treated as isolated technical tasks.
Regular reviews and independent assessments can help confirm that security controls remain effective. Businesses should test backup recovery procedures, evaluate incident response readiness, and monitor important changes across their SAP landscape. Documented policies provide guidance for administrators and business users. Continuous improvement is essential because enterprise environments, operational needs, and cybersecurity threats change over time.
How Can Organizations Build an SAP Cyber Security Strategy?
Developing an SAP cybersecurity strategy starts with assessing the current environment and identifying important business risks. Organizations should examine applications, infrastructure, user permissions, integrations, and existing protective controls. This assessment provides a starting point for setting realistic security priorities. Businesses can then create a roadmap that addresses critical vulnerabilities while supporting operational requirements.
A successful strategy requires collaboration between cybersecurity teams, SAP administrators, business process owners, and organizational leadership. Technical experts understand system configurations, while business teams can explain operational dependencies and sensitive workflows. Combining these perspectives improves risk assessment and security decision-making. Clear ownership ensures that important tasks, including patching and access reviews, are completed consistently.
Security performance should be evaluated through meaningful indicators rather than the number of security tools installed. Organizations might monitor overdue critical patches, excessive privileged access, unresolved findings, and incident response readiness. Regular reporting helps leadership understand progress and identify areas requiring additional investment. A well-maintained strategy supports resilience, compliance efforts, and long-term confidence in SAP operations.
Conclusion
SAP cyber security plays an essential role in protecting the enterprise applications that support modern business operations. From financial systems and customer records to cloud platforms and supply chain processes, SAP environments contain information that requires appropriate protection. Understanding what SAP cyber security is helps organizations recognize potential risks and implement safeguards that support secure, reliable operations.
An effective SAP security approach combines identity management, role-based permissions, vulnerability management, data protection, security monitoring, and incident response planning. Each component addresses different risks within the technology environment. Organizations should also consider cloud security responsibilities, connected applications, and regular employee awareness training. Coordinating these measures creates stronger protection than relying on individual tools alone.
As enterprise technology continues to evolve, SAP cybersecurity must remain an ongoing business priority. Regular assessments, timely updates, and continuous improvements help organizations respond to changing threats and operational requirements. By building a practical security strategy and maintaining appropriate controls, businesses can protect sensitive information, reduce disruptions, and support long-term digital resilience.
Frequently Asked Questions (FAQs)
What is SAP cyber security in simple words?
SAP cyber security means protecting SAP business software, sensitive information, and connected systems from unauthorized access and cyber threats. It involves access management, monitoring, security updates, and other protective measures.
Is SAP security the same as cybersecurity?
SAP security traditionally emphasizes user permissions, authorization roles, and access management. SAP cybersecurity covers these areas alongside broader threats involving applications, infrastructure, network connections, vulnerabilities, and potential security incidents.
What are the main components of SAP cyber security?
The main components include identity and access management, role-based authorizations, vulnerability management, encryption, secure integrations, security monitoring, and incident response. Together, these controls help protect SAP applications and business information.
Does SAP provide built-in cybersecurity features?
Yes, SAP products provide various security capabilities, including authorization controls, authentication options, logging, and data protection features. Their availability and configuration differ by product, and organizations remain responsible for implementing appropriate safeguards.
Is SAP cyber security a good career?
SAP cybersecurity can be a valuable career path for people interested in enterprise technology and information security. Relevant skills include SAP authorizations, identity management, risk assessment, security monitoring, and understanding business processes.